A machine ships to a customer's new plant. Cable trays and power distribution are finished; broadband is not. The plan changes at the last minute: the router in the cabinet takes a SIM card and the machine reaches the internet on its own. Once that proposal goes over, the customer IT team answers with one question: does going cellular make this less secure than pulling a cable?
The question usually draws "more secure" or "less secure," and neither answer is quite right. Set against an Ethernet router, a 5G cellular router does not differ in security grade. What differs is where trust sits. With a wired line, the campus gateway is the boundary. With cellular, the boundary moves onto the carrier network and onto that SIM card. The same holds for a 4G cellular router. Keep the leg that gets replaced separate from the few things that get added, and the answer falls into place.
It replaces one leg only, site egress to the carrier. Nothing changes on the stretch from the router ports back to the PLC, the HMI, and the supervisory computer. Whoever can plug into a port inside the cabinet, and whichever devices can reach one another across the cell, stay exactly as they were with a leased line. Swapping the egress method does not quietly settle the standing internal items: whether idle ports are disabled, whether legacy services on the machine still owe a patch, where the maintenance laptop gets plugged in.
The first is that the SIM becomes a credential that can be lifted out. With the cabinet door unlocked and the card moved into another device, what the network sees is a terminal that looks legitimate. Handling lands in two places: a cabinet lock and an inventory sheet with each card registered to a device number, plus refusing to read "it connects" as "it is trusted."
The second is that the APN type decides which path traffic takes. A public card leaves through the carrier's shared exit. IoT cards and private-network cards run over a dedicated channel on the carrier side, with data never touching the public internet. Documentation for the USR-G816 lists support for APN and VPDN cards. That has to be settled with the carrier when the card is ordered; finding out on site means reopening the request.
The third is an extra bill that can be spent. Cellular is metered by volume, and the first thing to shift when equipment misbehaves is the traffic curve, ahead of any alarm. Alarms for device offline, weak signal, and data limit exceeded support email and SMS delivery on the USR-G816. A threshold set at 70 to 80 percent of the plan costs less than chasing an overage after the fact.
The same concern applied to Wi-Fi usually raises two things: a broadcast SSID, and a password the whole shift knows. With cellular egress there is no such shared secret on site. A terminal has to clear authentication on the SIM side before it joins.
That does not mean discarding the wireless side. Local Wi-Fi stays practical for commissioning and for inspection work carried out next to the equipment, kept inside one bound though: enabled when it is needed, SSID switched off when it is not.
Cellular lines typically receive private or carrier-grade NAT addresses, in the 10.x and 100.64.x ranges, so connections initiated from the public internet never arrive at the device. The smaller exposure is genuine: a port scanner is aimed at an address with no inbound ports open.
The tradeoff is that remote maintenance loses the option of one more port mapping, and the device has to build the outbound path itself. Three routes all hold up. The device acts as a VPN client dialing toward a self-hosted server. The DM platform opens the router's built-in web page directly, which the official wording covers without requiring a private network or a public IP. Where sites multiply, the DM platform's remote networking joins the two internal networks. The USR-G816 supports PPTP, L2TP, IPSec, enhanced OpenVPN, and GRE; enhanced OpenVPN reaches three servers and also serves as one, and .ovpn with PKCS#12 files import in a single step.
Once the tunnel is up, arriving and seeing everything are still two separate matters. Destinations are permitted one entry at a time by address and port, and everything else falls to deny by default. That boundary does not move because the link underneath changed.
Run the same list against an installation where Ethernet carries the traffic, and most entries have nothing to do with the medium: egress destinations written out as a list, remote maintenance over a tunnel instead of a public port, machine areas separated from the terminals people use. Only two items genuinely vary with the medium, and both belong to cellular: whether the card gets registered, and whether the APN is a private-network one. The variable is not cellular versus copper. It is whether the boundary lands on the same device.
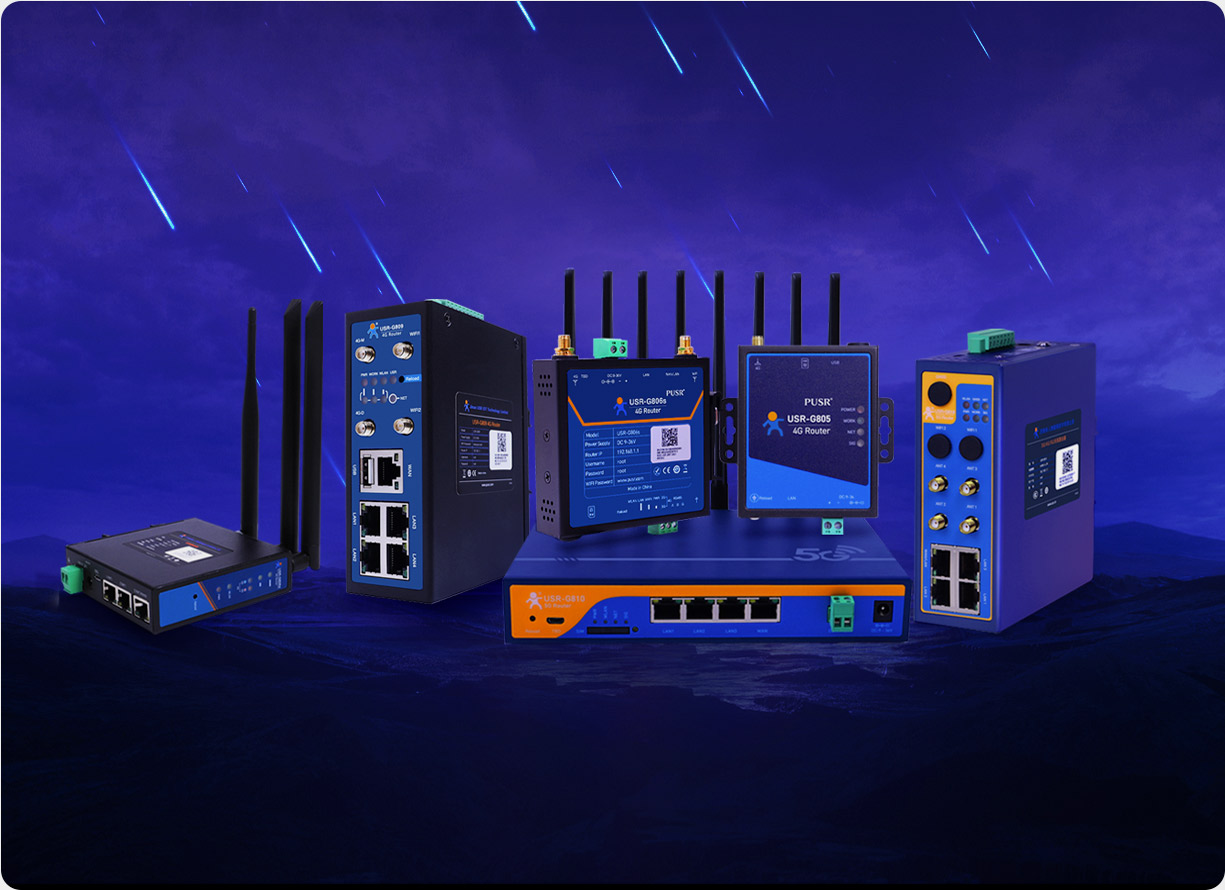
USR-G816 suits deployments that want 5G. Dual-mode 5G SA and NSA, dual SIM with the second slot available as an embedded eSIM to avoid dead spots across carriers, and automatic switching among Ethernet, cellular, and Wi-Fi as backup. Firewall, NAT, DMZ, port forwarding, and access restriction are all present, and RS232/RS485 terminals take older instruments that only kept a serial port. Power is DC 9-36 V with reverse-polarity protection, the metal housing is rated IP30, the operating range runs -35 to 75 degrees Celsius, and mounting is DIN rail or wall.
The USR-G806w handles small 4G points where cabinet space is tight. A Qualcomm chipset covers both controller and cellular module, and the three internet paths, cellular, wired, and Wi-Fi, switch freely as backup for one another, with the same five VPN protocols and enhanced OpenVPN. Dimensions come to 104 x 102 x 28 mm, mounting is DIN rail or wall, redundant power runs through both terminal block and DC jack, the card is Mini SIM (2FF), and the range is -20 to 70 degrees Celsius.
USR-G809s fits sites that carry Ethernet as the primary link and keep cellular only as backup: 2 x WAN/LAN plus 6 x LAN plus 2 x SFP, with one SFP shared against a copper port, dual Nano-SIM with SIM2 built in as an eSIM, independent VLAN subnet division, and all five VPN protocols. Paired with the DM platform's remote networking it links two internal networks even with no public IP in place. Wide-range DC 9-60 V with reverse-polarity protection, DIN-rail mounting.
What changed is the stretch of line carrying traffic out. What stayed put is where the boundary belongs. Treat a 5G cellular router and a 4G cellular router as boundary devices to be configured rather than as a card that supplies internet, and that question from customer IT has something concrete behind it.
1. Is cellular more secure or less secure than Ethernet?The two are not measured on the same scale. Cellular replaces only the outgoing leg; the internal network is untouched. The difference is that trust lands on the carrier network and on that SIM card.
2. With NAT in front of it, what else is needed?NAT blocks connections started from outside. Traffic the equipment initiates outward is permitted by default. What carries weight is the list of permitted egress destinations, plus running remote maintenance through a tunnel.
3. What happens if the SIM card is taken out?The card is the credential. Placed into another device, what the network sees is a terminal that looks legitimate. Alongside the cabinet lock and inventory sheet, a private-network card is worth considering at order time, with the traffic alarm threshold set at 70 to 80 percent of the plan.
4. What separates an IoT or private-network card from an ordinary one?An ordinary public card leaves through the carrier's shared exit. IoT cards and VPDN private-network cards run over a dedicated channel on the carrier side, with data kept off the public internet. Confirming this with the carrier belongs before ordering.
5. With no public address, can the line still be maintained remotely?Yes. Let the device reach outward instead: a VPN tunnel, opening the router's built-in web page through the DM platform, or DM remote networking. None of the three asks the device itself to hold a public IP.
6. Is there a security difference between 5G and 4G?Core security mechanisms sit close together. The difference shows up mainly in bandwidth and latency, so the choice tracks uplink requirements and how the network will look over the next few years.
7. Wi-Fi on the machine opens another door, does it not?Switch off the SSID when it is not needed. Where local commissioning requires it, keep wireless confined to that single purpose rather than letting it carry coverage for the whole site.
8. How does a line or account problem become visible?Alarms for device offline, weak signal, and data limit