A production line ships with one router in the cabinet and four or five devices behind it: a PLC, an HMI, a barcode reader, a PC still running older host software. The requirement list is short. Those few machines need to talk to each other. They need to reach a specific license server. They must not reach arbitrary addresses on the internet. Ports have to be gigabit. Wireless is not needed. Budget is limited.
Lists like this rarely get an answer in buying guides aimed at home equipment. Consumer units offer parental controls inside a phone app, not per-device restriction of destination addresses. On the industrial side, every line translates into a concrete item, and most of them land on the same 4G cellular router.
When wireless is explicitly not needed, radio specifications drop out of the selection criteria. What gets saved is often not the price gap between models, but the cost of an access point, a run of cabling, and one extra round of acceptance testing.
The absence of an SSID only removes one entry point. Machines in the cabinet still initiate outbound connections on their own, so the egress side still needs to be governed. Budget freed up here belongs on port count and power headroom.
Port count follows a simple rule: device count plus uplink, plus one or two spare for service. Five machines and one uplink means six ports. Whether a model fits comes down to how many LAN ports it actually has.
Compact units often provide only three LAN ports. Four machines fill it, the fifth pushes a second switch onto the bill, and the low-cost option ends up priced as two devices.
Within a single series, some models come with 10/100 Mbps auto-sensing ports while others carry 10/100/1000 Mbps. Requiring gigabit rules out the former. Those suit small sites with two or three devices where gigabit was never a stated need.
There is also no reason to over-specify. Cellular uplink does not run that wide; LTE uplink sits an order of magnitude below gigabit. In lists like this one, gigabit serves traffic inside the cabinet: machines exchanging data, host software pushing batch program downloads. The deciding question is whether heavy lateral traffic exists on site.
"These machines talk to each other" looks like it contradicts "no internet access," but the two sit in different places. Firewall rules act on the forwarding path, governing traffic that crosses subnets or leaves for the outside. Two devices on the same LAN reach each other through Layer 2 switching, which never touches that rule set. Restricting egress while keeping local connectivity is not a conflict.
The exception is segmentation. Move those machines into separate subnets or VLANs and cross-subnet traffic needs an explicit permit. Keeping everyone in one subnet is simpler, and restrictions concentrate on the single egress rule. Acceptance testing is straightforward too: machines on the allowed list cannot reach the internet, yet still ping each other.
Whether this kind of policy is achievable depends on whether the rule table carries enough fields: source MAC or source IP, destination address, protocol, port, action, and whether priority order can be rearranged. Missing fields or a fixed order leave the policy stuck at allow-all or deny-all. Ask for a screenshot of the rule page before ordering.
Two defaults deserve a line in the handover document. Source MAC and source IP are mutually exclusive; when matching on MAC, the source IP field must stay empty, and filling both never produces a hit. The catch-all deny goes last, and changes take effect only after a reboot. Where the destination address is not fixed, a domain whitelist works instead, with one caveat: enabling the whitelist without adding any entry blocks every domain, so it stays disabled until entries are in place.
Anything not on the list is fair game: PoE, radio that will never be used, double the ports needed, a managed switch.
What is not fair game are the items that decide whether a truck rolls. Cabinet 24 V dips when motors start and stop, so a wide input range with reverse-polarity protection says more than the nominal voltage. A watchdog resets the device by itself instead of waiting for someone to cycle power. Wide temperature ratings and a metal housing answer the heat that builds up inside an enclosure. DIN-rail mounting removes the need to drill new holes in the backplate. Add remote management covering parameter changes, reboots, and firmware upgrades, and one whitelist edit no longer costs a site visit.
For deliveries into Europe, cyber-security requirements deserve a check alongside the usual CE marking. EN 18031 is the EU standard covering cyber security for radio equipment, several PUSR models are listed under it, and confirming the target model appears on that list belongs before the order rather than after it.
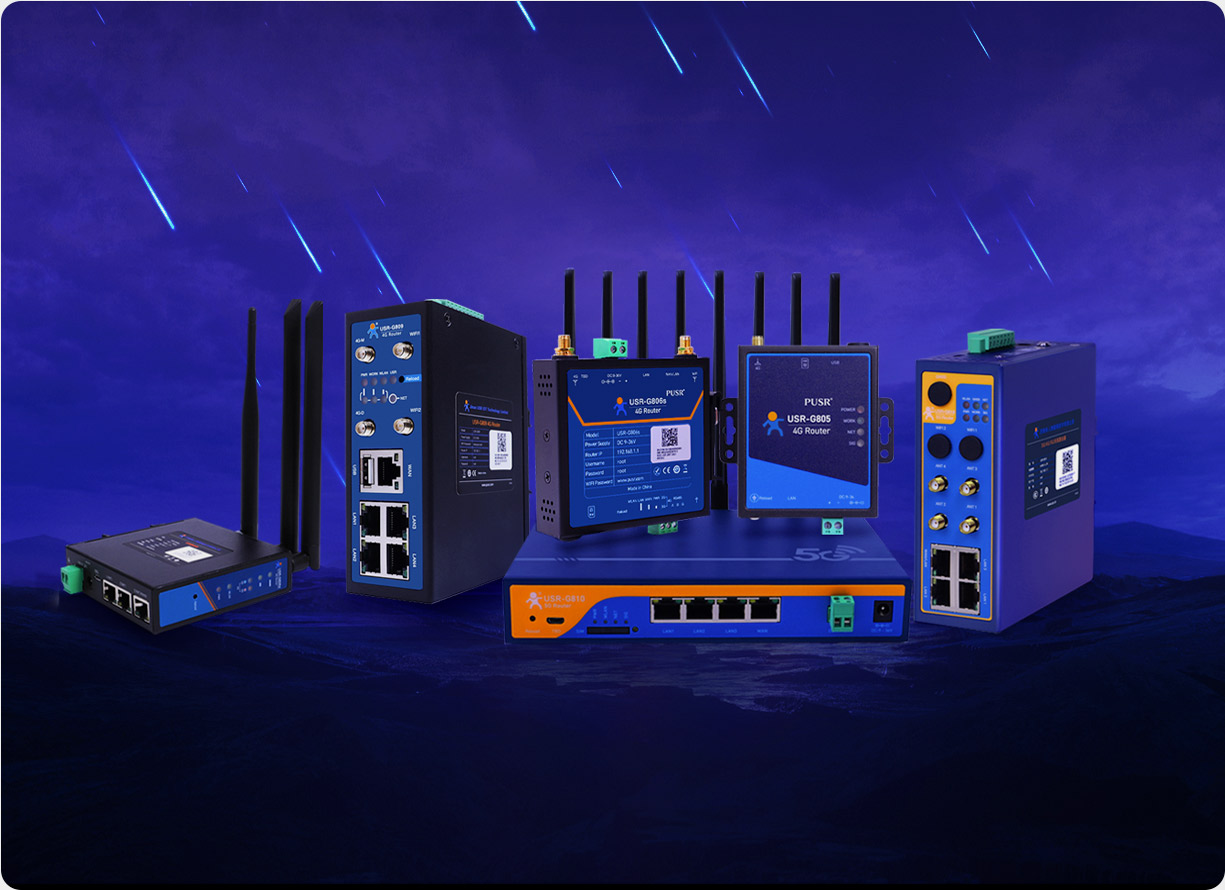
USR-G809s provides 2 x WAN/LAN, 6 x LAN, and 2 x SFP, where one SFP slot is an either-or choice against a WAN/LAN copper port. RJ45 ports negotiate 10/100/1000 Mbps and the SFP slots are gigabit optical, with 1.5 kV network isolation protection. Six or more LAN ports absorb five machines plus an uplink without an extra switch, making it the closest fit on this list. The aluminium housing is rated IP40 and mounts on DIN rail or lies flat. Power is DC 9-60 V through a terminal block with reverse-polarity protection, -25 to 75 degrees Celsius, with a built-in watchdog.
USR-G816 suits cases where the uplink side carries more load: 5G NR SA/NSA dual mode on a Qualcomm X62 module, with WAN failover switching to a backup link automatically. Ethernet is 1 x WAN, configurable as LAN, plus 3 x LAN, all gigabit; DC 9-36 V with reverse-polarity protection, -35 to 75 degrees Celsius, metal housing rated IP30. Three LAN ports means five machines will most likely need a small switch added, which belongs in the total before comparing prices.
USR-G806w is the fallback rather than the front runner. Its ports are 10/100 Mbps auto-sensing, so it does not apply where gigabit is stated. It is compact at 104 x 102 x 28 mm, rated -20 to 70 degrees Celsius, with redundant power through an industrial terminal block and a DC jack, DIN rail or wall mounting, suited to small sites with few endpoints and tight cabinet space.
A short list turns into six items: port count, whether gigabit is required, whether rules reach MAC level, the fact that same-subnet traffic needs no extra rule, certification coverage, and which savings come back as site visits. For a small network of four or five wired machines, a 4G cellular router has a narrow job: bring the machines in, control the egress point, and leave the remaining adjustments to be made remotely.
1. Five machines plus one uplink: how many ports in total?
Six minimum, seven or eight preferred. Spare ports absorb a commissioning laptop and devices added later. Once every port is taken, expansion means buying a switch, which costs more than choosing a higher-port model up front.
2. The requirement says no wireless. Can radio specs be skipped altogether?
The specs can be skipped; the security side cannot. No SSID means one fewer entry point, but wired devices still initiate outbound connections, so egress restrictions remain necessary.
3. Will a whitelist block machines talking to each other?
No. Those rules act on the forwarding path, while two devices on the same LAN reach each other through Layer 2 switching without touching the rule table. An explicit permit is needed only when devices sit in different subnets or VLANs.
4. Is gigabit about uplink speed?
No. Cellular uplink sits well below gigabit, LTE uplink especially. Gigabit in requirement lists usually serves local exchange, on-site recording, or batch downloads, so the deciding question is how much lateral traffic exists.
5. Which rule fields are worth checking?
Source MAC or source IP, destination address, protocol, port, action, and whether priority order can be rearranged. Missing any one leaves the policy at allow-all or deny-all. Requesting a screenshot of the rule page is the fastest way to confirm.
6. What causes the most rework?
Two defaults. Source MAC and source IP are mutually exclusive, so the source IP field stays empty when matching on MAC. A domain whitelist enabled with no entries blocks every domain. Rule changes also need a reboot before taking effect.
7. Can the cheaper items be cut first?
PoE, unused radio, and excess ports can go. Cutting wide input range, reverse-polarity protection, wide temperature rating, watchdog, DIN-rail mounting, or remote management usually gets paid back later in site visits.
8. How is certification checked for EU delivery?
Beyond routine CE marking, cyber-security compliance needs a look. EN 18031 is the EU standard covering cyber security for radio equipment, several PUSR models are listed under it, and confirming the exact model appears on that list is easier before shipment than after it.